Platform
One system of record for your entire compliance programme
One system of record for your control environment — what each control is, who owns it, what evidences it, and whether it is holding up between audits.
Readiness assessment
Walk into the audit already knowing the outcome
A readiness assessment maps what you have against what the framework demands — before an auditor bills you to find out. Cornerstone runs that assessment continuously: every control mapped to every criterion, every gap named, every fix tracked to done.
Map your controls to the criteria
Bring your control set — ours, your previous auditor's, or your own — and map each control to the individual criteria it satisfies across SOC 2, ISO 27001, and HIPAA at once.
See every gap, stated outright
A criterion with no covering control is listed as an explicit gap. Nothing is averaged into a blended score that hides unsatisfied requirements.
Close gaps with owners and dates
Each gap becomes tracked remediation work with an owner and a due date. Evidence attaches to the control as you close it, so the fix is audit-ready the day it lands.
Capabilities
What the platform does
Grouped by the problem each part solves, rather than by which screen it lives on.
Controls and evidence
Control library
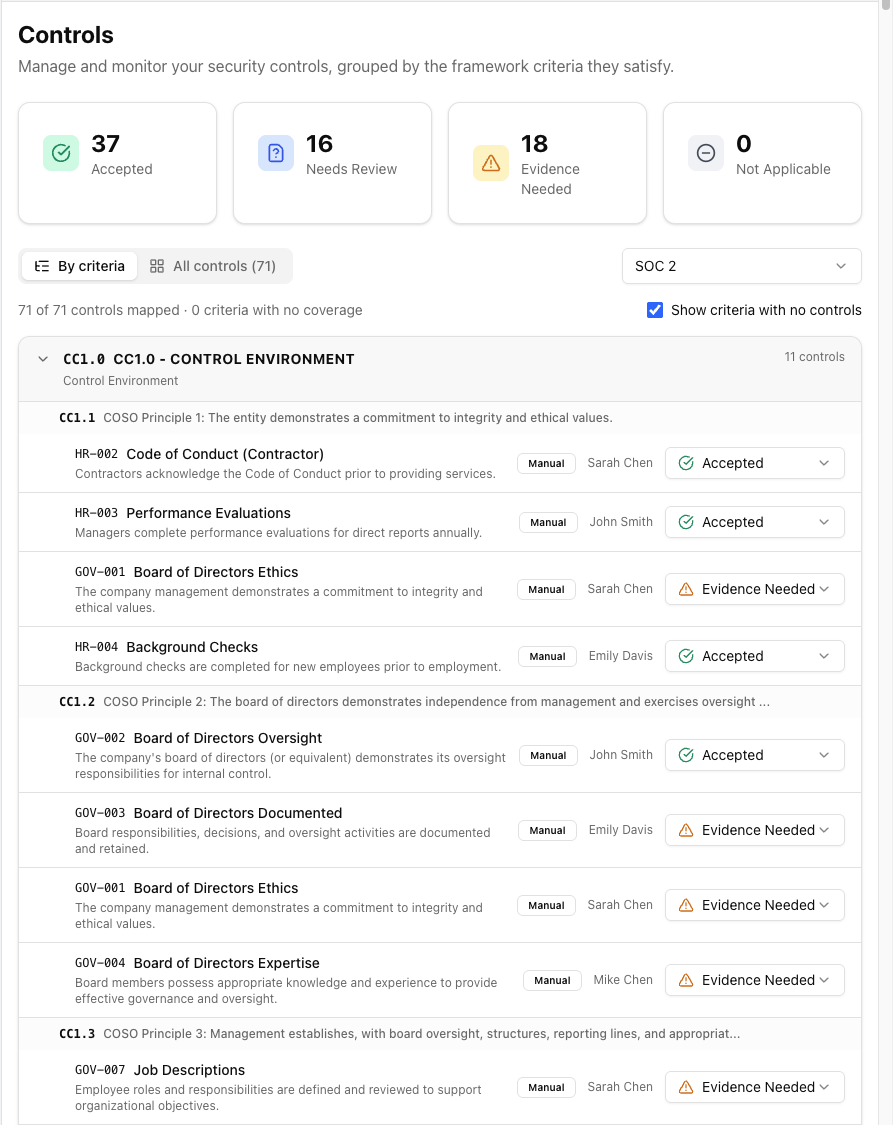
Every control with its owner, test frequency, implementation detail, and current status — mapped to the framework criteria it satisfies.
Evidence management
A register of what has been collected, which controls it supports, and what is close to expiry, so nothing lapses quietly between audits.
Continuous monitoring
Controls carry a test frequency and a next-review date. Work that is coming due surfaces before it becomes an audit finding.
Integrations
Connect the systems that already hold your evidence, so collection is not a quarterly scramble.
Framework readiness
Readiness by criterion
Progress against each individual criterion rather than one aggregate percentage, so you can see exactly which requirements are unsatisfied.
Multi-framework mapping
One control can satisfy criteria across SOC 2, ISO 27001, and HIPAA at once. Evidence gathered for one certification counts toward the others.
Gap visibility
A criterion nothing covers is shown as an explicit gap, not averaged into a comfortable score.
Risk and governance
Risk register
Scored risks with treatment plans, bulk import, and linkage to the controls that mitigate them.
Policy management
Policy library with version history and per-employee acknowledgement tracking.
Vendor risk
Third-party inventory with review cadence and the evidence supporting each assessment.
People and access
Personnel records
Onboarding, offboarding, and security training completion, kept audit-ready.
Access reviews
Periodic entitlement reviews with the reviewer, date, and outcome recorded as evidence automatically.
Change management
Code and configuration change records tied to the controls that govern them.
Working with your auditor
Auditor correspondence
Evidence requests and your responses live on the control itself, so the audit trail is the conversation — not a mail thread.
Request tracking
See every outstanding auditor request in one place, with who owns it and what is blocking it.
Scoped auditor access
Your auditor sees the engagement they are assigned to, and nothing beyond it.
Frameworks
Mapped to the criteria you are examined against
Readiness is tracked per criterion. A criterion nothing covers shows as an explicit gap rather than being averaged away.
Type I and Type II
All five Trust Services Criteria — Security, Availability, Confidentiality, Processing Integrity, and Privacy — down to the individual criterion.
Information security management
Annex A controls with statement-of-applicability tracking and surveillance-audit support.
Security and Privacy Rules
Administrative, physical, and technical safeguards for organisations handling protected health information.
Your own framework
Import a control set and map it to any criteria structure your programme requires.
Audit Workspace
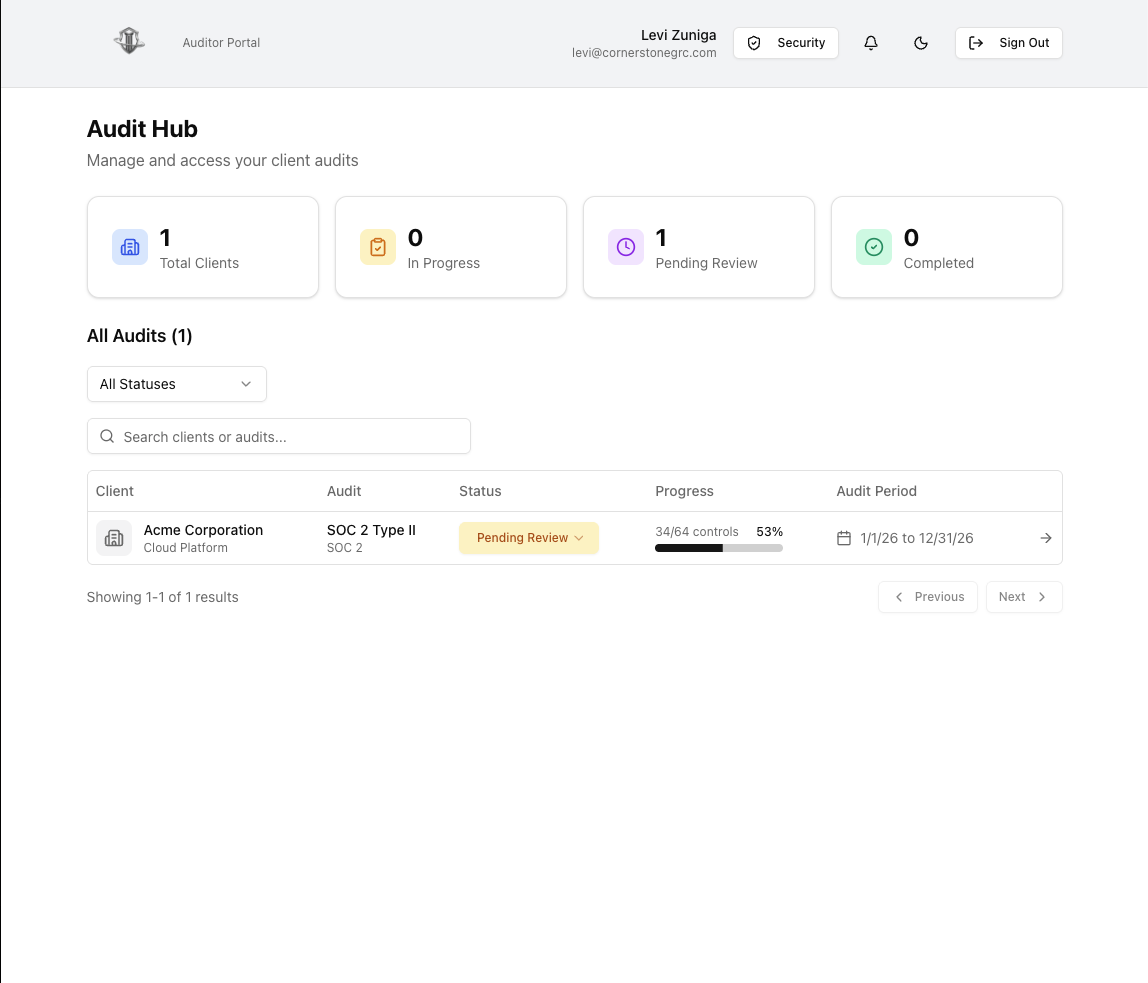
Fieldwork tooling for the firm conducting the audit. Most customers never touch it — it exists so your auditor can work directly against your control environment instead of a spreadsheet circulated by email.
Who this is for: Audit and assurance firms, and organisations whose internal audit function runs its own testing.
It is licensed separately and is not required to run a compliance programme on Cornerstone. If your audit firm brings its own tooling, the platform works exactly the same way.
Testing sheet as a control matrix
Rows sit under the criterion they satisfy, with the full criteria structure always visible — including criteria nothing covers.
Preparer and reviewer sign-off
Status is derived from signatures rather than typed. Segregation of duties is enforced, and editing tested work clears the attestation.
Report generation
Merge firm templates with signed-off results. Unresolved fields are listed, so a draft never ships with a silent blank.
Internal QA review
Assign review work across the engagement team, tracked separately from anything client-facing.
Common questions
See it against your own framework
A thirty-minute working session on your actual controls — not a slide deck.